Tie every physical asset to a verified owner.
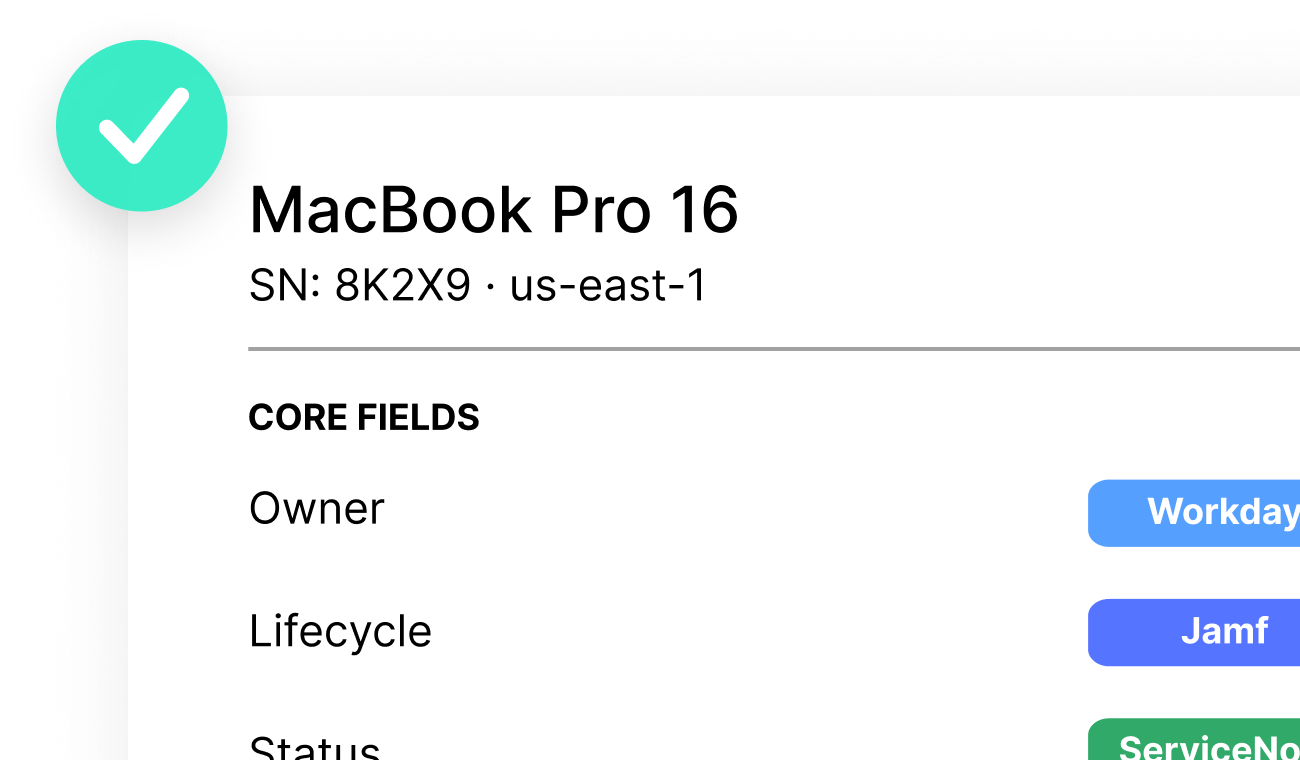
Each device record is built from connected endpoint, security, and ITSM sources, covering owner, location, and lifecycle state, with ghost assets surfaced for resolution.
See Hardware Asset Management
Solutions / Asset Risk & Security
ASSET RISK & SECURITY
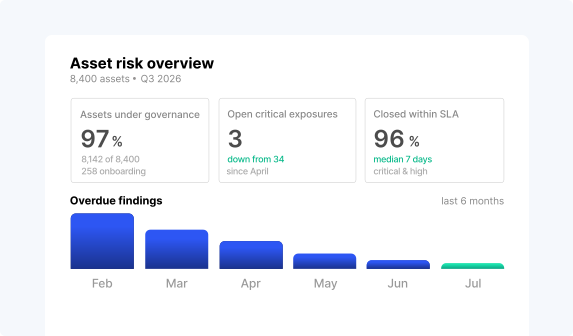
Attach an owner, a lifecycle state, and a clear next step to every risk your security tools surface, so nothing stalls between detection and resolution.
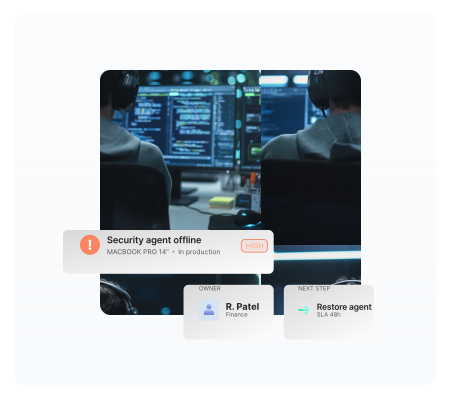
Oomnitza reconciles what your EDR, scanners, and identity tools each know into one governed record, so every exposure becomes something you can assign and close.
TRUST
A finding tells you what’s wrong. It doesn’t tell you who owns the device or what state it’s in. Oomnitza supplies that from a verified record, so every exposure arrives ready to act on.

ACT
Most exposures stall while someone tracks down the owner and the right response. Oomnitza automatically routes it to the owner, kicks off remediation, and locks down the device the moment it slips out of policy.

LEAD
Security stops chasing ghosts and starts closing real gaps, and leadership answers exposure, ownership, and remediation questions from evidence instead of estimates.
PRODUCTS

Each device record is built from connected endpoint, security, and ITSM sources, covering owner, location, and lifecycle state, with ghost assets surfaced for resolution.
See Hardware Asset Management
Asset records from every connected source are reconciled and enriched with lifecycle context, so the accuracy downstream systems depend on holds as the environment changes.
See Data Integrity Engine


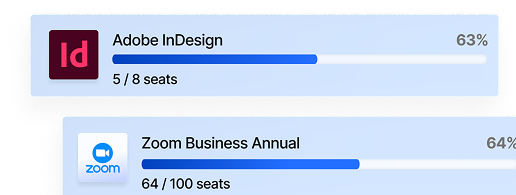
Every application, installed or SaaS, is matched to its entitlements and actual usage, with tools acquired outside IT surfaced and access tracked for each.
See Software Asset Management

When an asset has no owner or falls out of policy, it goes straight to the right person to handle, not into a queue. Unknown devices are held safely until someone claims them, and every step is recorded.
See Automations & Workflows

CUSTOMER STORY
 |
|
| “Thanks to Oomnitza, we’ve gained complete visibility on all of our endpoint devices. This empowered us to make informed procurement decisions, particularly as we prioritize cost and process efficiency.”
– Vice President, Technology Services, Leading Online Used Car Dealer
|
|
$640,000Annual capital expenditure savings on hardware assets |
100%Compliance rating with NIST & SOC 2 requirements |
| READ FULL STORY | |
INTEGRATIONS
Endpoint, identity, HR, and security each know something different about the same asset. Oomnitza reconciles what they know into one verified record.
Asset visibility means knowing what technology assets exist in your environment. Asset ownership means knowing who is accountable for each one. Most organizations have visibility into what exists but lack verified ownership context, which is why security findings stall, financial decisions are made on incomplete data, and operational questions require manual investigation to answer.
Ownership gaps accumulate because asset records are not automatically updated when circumstances change. Employees leave, transfer, or change roles without triggering ownership updates. Devices are deployed without formal intake. Software is procured outside IT. Each event creates an asset without a current, verified owner. Without a system that detects and routes these gaps automatically, unowned assets accumulate silently until something forces an audit.
Oomnitza connects to HR, identity, MDM, ITSM, and procurement systems and reconciles what each one says about asset ownership continuously. When an employee leaves or changes roles, Oomnitza detects the event and updates ownership records automatically. When a new device is deployed, Oomnitza triggers an intake workflow that assigns an owner before the asset becomes active.
Security findings can only be actioned when there is a verified owner to route them to. When a CAASM or vulnerability management tool surfaces a coverage gap or out-of-policy device, Oomnitza provides the ownership context needed to create an assigned remediation workflow rather than an unresolved alert. Security teams stop seeing the same findings month after month because findings now route to people rather than queues.
Asset discovery tells you what devices and software exist at a point in time. Asset visibility tells you what exists, who owns it, what its lifecycle state is, what it costs, what it connects to, and whether it is in compliance. Continuously. Discovery is the starting point. Visibility is the governed, continuously current state that makes every decision about the asset defensible.
When Oomnitza detects a device with no ownership record, not enrolled in MDM, or absent from procurement data, it places the device in a governed unassigned state and triggers an ownership inquiry workflow. The device is held pending investigation with the finding routed to the appropriate team for determination and disposition.
Oomnitza scans purchase orders, invoices, and expense reports against a library of known software signatures to identify applications being paid for but absent from the managed software inventory. Shadow IT findings are routed to the appropriate owner for review and either brought under management or flagged for removal.
When every asset has a verified owner and current lifecycle state, financial records stay aligned with operational reality. Depreciation reflects actual asset status. Cost center allocations update when assets change hands. Retired assets close financially at disposition rather than persisting on the balance sheet. The result is more accurate technology spend reporting and procurement decisions grounded in what is actually available.
Most organizations see a continuously current, ownership-enriched asset record within weeks of connecting their primary data sources. The initial reconciliation typically surfaces existing gaps including unowned assets, ghost records, and shadow IT that have been accumulating without detection. Accuracy then maintains continuously rather than degrading between cleanup cycles.
Oomnitza connects to endpoint management tools like Jamf and Intune for device state, identity providers like Okta and Microsoft Entra ID for ownership verification, ITSM platforms like ServiceNow for operational context, HR systems like Workday and BambooHR for workforce changes, and procurement tools like Coupa and Ariba for purchase records. Oomnitza has over 1,500 connectors and does not require agent deployment.
Reach out to see what’s possible.