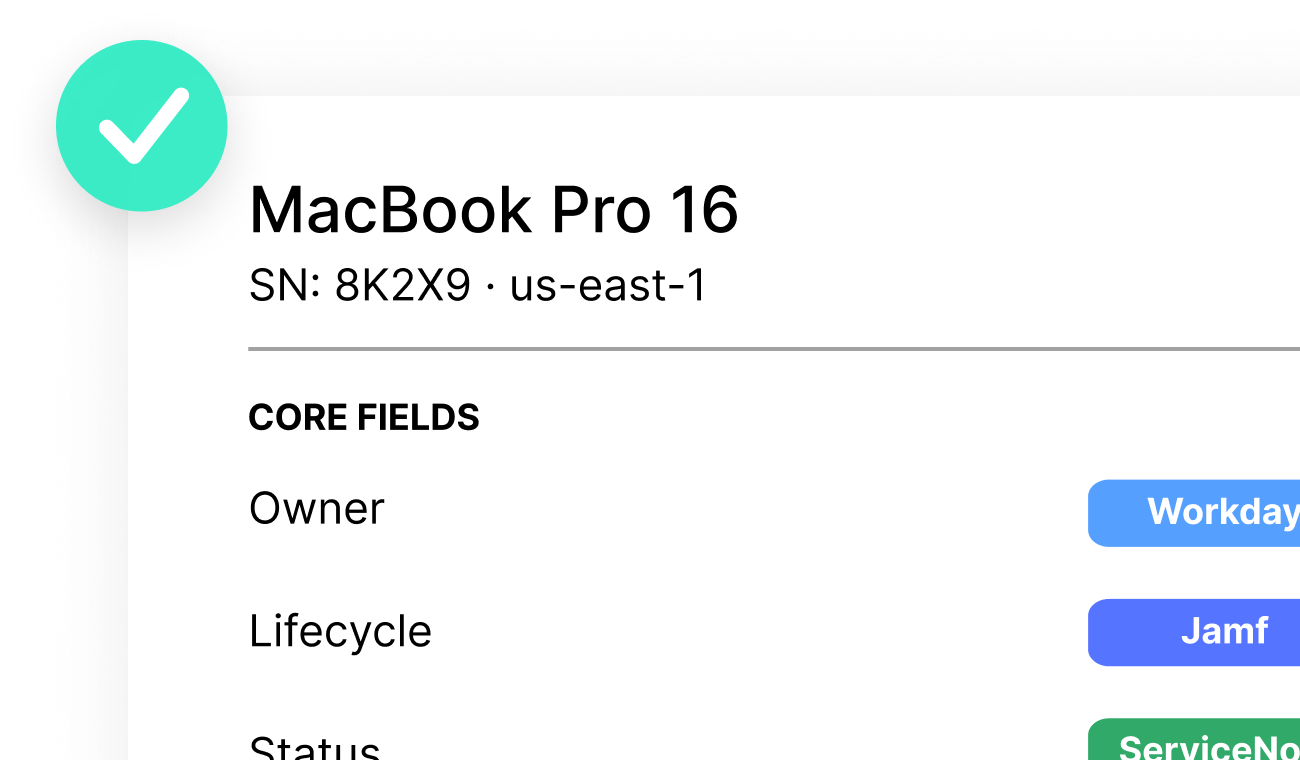
Provision, track, and recover every device you assign.
Assignment triggers from the HR event at onboarding, every custody change is logged while the device is in use, and a return workflow recovers it at offboarding.
See Hardware Asset Management
Solutions / Onboarding & Offboarding
ONBOARDING & OFFBOARDING
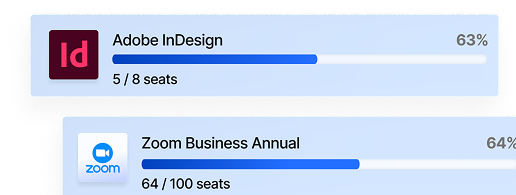
Recover idle licenses, right-size renewals, and surface shadow spend.
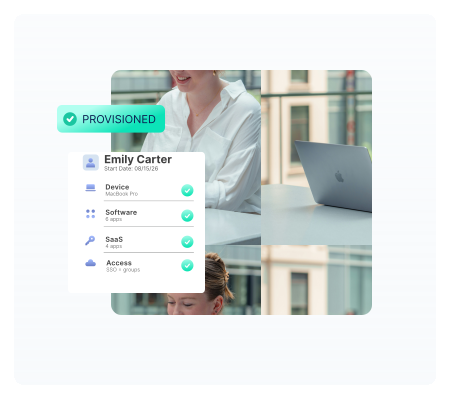
Oomnitza connects HR, IT, security, and procurement into a single governed workflow so every joiner, mover, and leaver transition happens completely, consistently, and with a full audit trail.
TRUST
HR, procurement, MDM, identity, and ITSM each hold part of the employee asset picture. Oomnitza connects them so every provisioned device, license, and access right is visible in one place.

ACT
When an HR event fires, Oomnitza acts across every connected system automatically. Joiners get everything they need before day one. Movers get updated access and assets at the moment of transition. Leavers have everything recovered and revoked before they walk out.

LEAD
New hires are productive on day one, exits close access and recover devices on their own, and freed licenses keep spend in check. When every transition runs itself, IT absorbs changes without scaling the team or the risk.

PRODUCTS

Assignment triggers from the HR event at onboarding, every custody change is logged while the device is in use, and a return workflow recovers it at offboarding.
See Hardware Asset Management
Lifecycle rules fire at every offboarding, reclamation, and policy exception, so each action leaves a timestamped, owner-attributed record without anyone standing up a compliance project.
See Automations & Workflows


When someone joins, changes roles, or leaves, their software access is set, adjusted, or removed to match, so no one waits on day one and no one keeps access they no longer should.
See Software Asset Management

Employees request what they need from one catalog. Every request is checked against inventory, entitlement, and policy before it's approved, then fulfilled on its own. Access is fast, and always in bounds.
See Request Portal
CUSTOMER STORY
 |
|
| “The team at Oomnitza helped us automate the S2R ‘zero touch’ secure offboarding process. As a result, we were able to recover a high volume of employee-issued endpoints, as well as dramatically reduce the risk of unauthorized access to company systems and data. I highly recommend Oomnitza for anyone looking to streamline and secure their IT offboarding process.”
– Vice President, IT Services, Major Home Improvement Retailer
|
|
96%Time reduction for complete access revocation |
98%Successful recovery of endpoints from departing employees |
| READ FULL STORY | |
INTEGRATIONS
HR, identity, MDM, ITSM, and procurement each control a piece of the employee transition. Oomnitza connects them so every system acts from the same event.
IT onboarding and offboarding automation means replacing manual coordination across HR, IT, security, and procurement with governed workflows that trigger automatically when an employee joins, changes roles, or leaves. When an HR event fires, Oomnitza provisions devices, licenses, and access automatically at onboarding and reverses all of it completely and in the right order at offboarding with every step logged for audit and security purposes.
Manual joiner and leaver workflows fail because they depend on people remembering to act across systems that do not communicate with each other. IT has to manually trigger device orders, license requests, and access provisioning separately and at offboarding, manually revoke access across every application the employee used. When any step is missed, the result is a delayed first day, a ghost account, an orphaned license, or an unreturned device.
When HR systems indicate a new hire, Oomnitza triggers a complete provisioning workflow automatically: ordering the device, provisioning licenses based on role and department, activating access in identity systems, creating ITSM tickets, and notifying the manager. Every step runs without IT having to coordinate manually across systems. The employee arrives to a complete setup rather than a queue of pending requests.
When HR systems indicate an employee departure, Oomnitza triggers a complete deprovisioning workflow that revokes access across connected applications, reclaiming licenses, locking devices, generating shipping labels for remote device return, checking for legal holds, and logging every action with a timestamp. The workflow runs in the right order without IT manually coordinating across systems. Nothing lingers after the employee has left.
When an employee changes roles or departments, Oomnitza detects the HR event and updates asset assignments, license entitlements, and access rights to reflect the new role. Access from the previous role is revoked automatically. This prevents privilege accumulation. Employees retain access from every previous role alongside their current one. This is one of the most common access governance findings in security audits.
ITSM platforms manage tickets and workflow routing but they depend on accurate asset and access data being fed to them from upstream systems. When that data is incomplete, tickets get created for licenses that are already available, devices that are already assigned, or access that was never revoked. Oomnitza governs the asset and access layer that feeds ITSM workflows, ensuring every action is based on verified current data rather than assumptions.
Oomnitza connects to every identity provider and application in scope and revokes access across all of them when an offboarding event fires. License reclamation runs at the same time so unused seats return to the available pool. Every action is logged with a timestamp so security teams have a complete record of what was revoked and when.
When a remote employee offboards, Oomnitza automatically generates a shipping label using the employee’s home address and sends it to their inbox along with a manifest of devices and accessories to return. The return is tracked through the shipping provider and the device record updates when the device is received. This replaces the manual process of IT emailing departing employees and following up when devices go unreturned.
Most organizations have core joiner and leaver workflows running within weeks of connecting their HR, MDM, identity, and ITSM systems to Oomnitza. Oomnitza has over 1,500 agentless connectors and prebuilt workflow templates for common joiner, mover, and leaver scenarios. The initial deployment typically surfaces workflow gaps including orphaned licenses, ghost accounts, and unreturned devices that have been accumulating without automated governance.
Oomnitza connects to HR systems like Workday and BambooHR for lifecycle events; identity providers like Okta and Microsoft Entra ID for access governance; MDM tools like Jamf and Intune for device management; ITSM platforms like ServiceNow and Jira for ticket creation; and collaboration tools like Google Workspace and Microsoft 365 for document reassignment. Oomnitza has over 1,500 connectors and does not require agent deployment.
Reach out to see what’s possible.